00Haxurn
Samson Tesfaye
Tech entrepreneur · trader · builder
- Ventures
- Forex trading
- Software
- Security
- Design
- Music
Current focus: Co-founder & CTO, Solvix Labs PLC · trading FX since 2024
01About
Founder by day, trader at the open, producer on weekends.
I co-founded Solvix Labs PLC and build the products it sells. I trade forex, ship software with security built in, and produce music.
- Codename
- Haxurn
- Base
- Addis Ababa, Ethiopia
- Since
- 2024
- Runs
- Solvix Labs PLC
- Trades
- FX majors · gold
Africa/Addis_Ababa
Background
My name is Samson Tesfaye. Online I go by Haxurn. I am a tech entrepreneur in Addis Ababa. I run a company, I trade the currency markets, and I still write a lot of the code myself. Each of these feeds the others.
I taught myself. I started with HTML and CSS, then moved into security. In 2024 I learned Python, started competing in capture-the-flag events, and joined the red team at INSA, Ethiopia's national security agency, where I tested real systems with permission. In mid 2024 I left INSA to build my own things.
Today I am co-founder and CTO of Solvix Labs PLC, which we started in mid 2024. We build Axova, a platform that lets Ethiopian merchants sell online, in store, and through a marketplace from one account. Also in 2024 I started trading forex: majors and gold, charted on TradingView and executed on MetaTrader 5, with some strategies automated in code. On weekends I produce music.
·Manifesto
Operator doctrine
I. Read the binary, then the specification.
Documentation says what a system is meant to do. The code says what it actually does. Before I trust a system, I read the code, even if that takes a weekend and a debugger.
II. Exploit to understand. Build to protect.
Attacking systems shows you weaknesses that defenders rarely see. I do both, but the code I write exists to close doors, not open them.
III. Small improvements, compounded.
A stricter check. A trade sized to the risk, not the hope. A plugin released on a quiet Sunday. In a company, in the markets, and in code, small wins compound, and a year is worth the sum of them.
Haxurn · Addis Ababa, Ethiopia
02Projects
Selected work
Client sites, my own product, libraries, and upstream fixes, with proof for each.
5 Project · 2 Plugin · 3 Upstream contribution
YES Multimedia
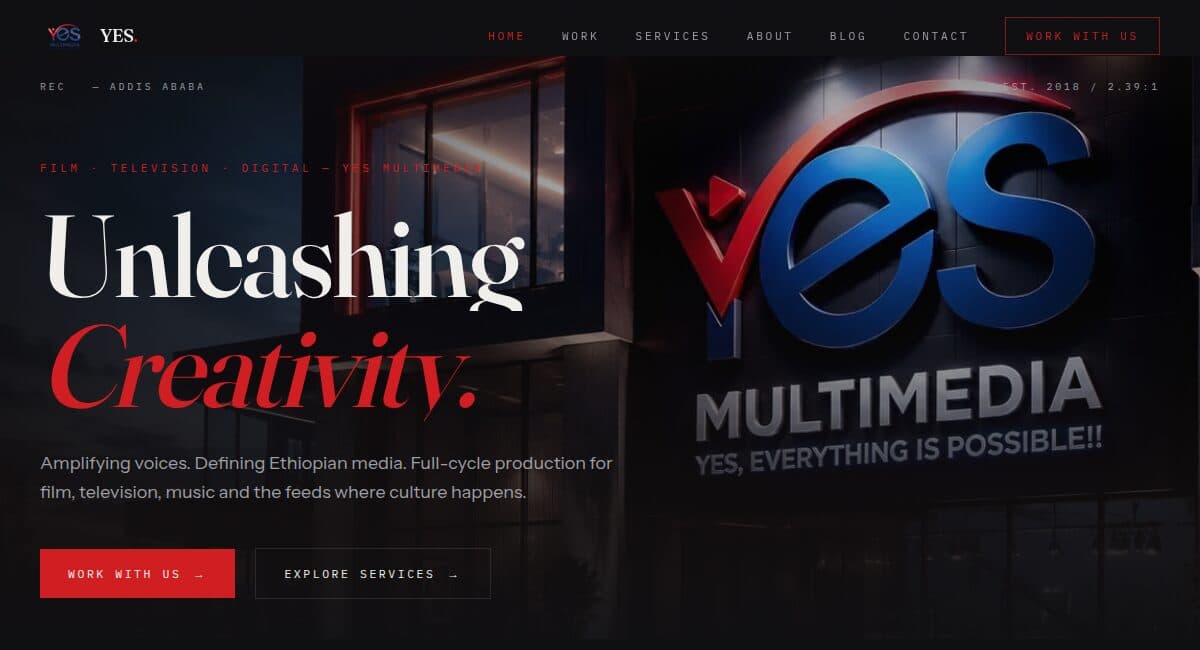
Website for a full-service film and video production company in Addis Ababa.
YES Multimedia makes television, commercials, music videos, and live broadcasts. I designed and built a site that puts their work first: film stills open every section, and a producer can reach any showreel in one tap.
Design + buildShipped
- TypeScript
- Next.js
- Editorial design
Shipped sites03
Axova
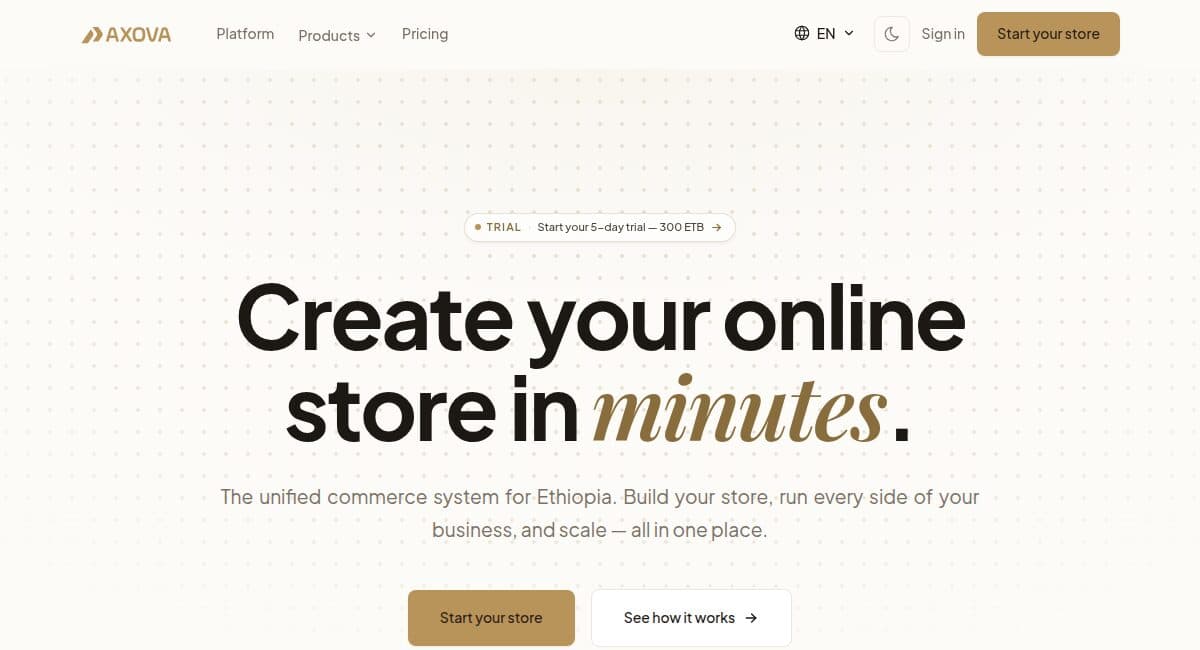
ProjectCo-founder & CTO · Solvix Labs PLCOngoing
A unified commerce platform for Ethiopia: online storefront, point of sale, marketplace, and delivery.
- TypeScript
- Next.js
- Commerce
- Monorepo
Mamy Opticians
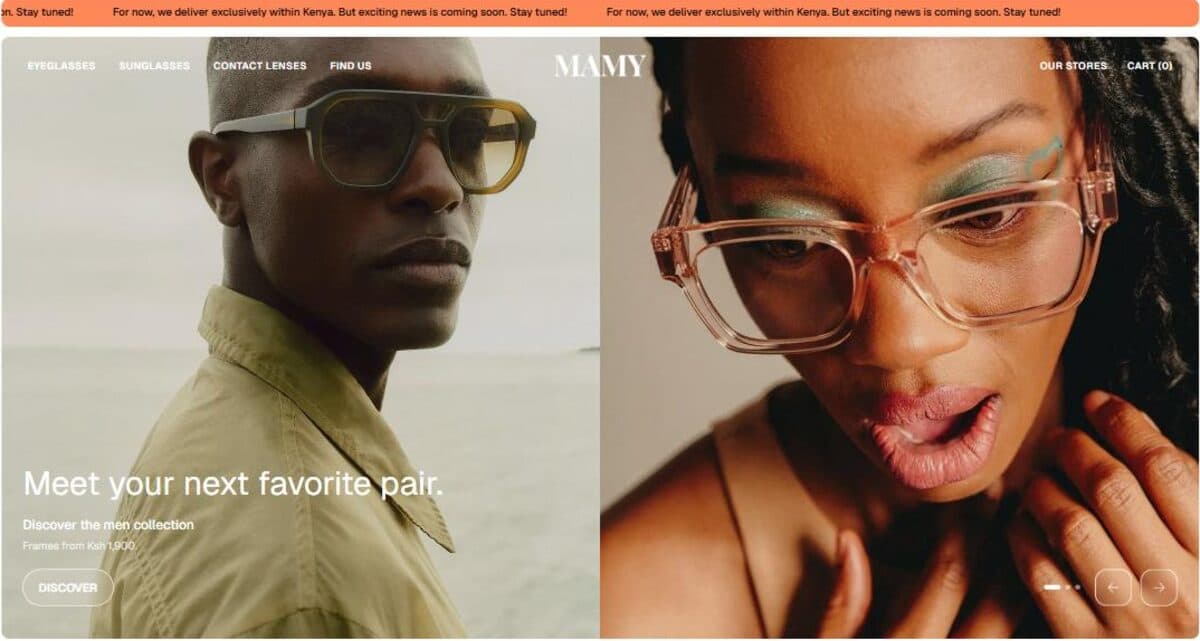
ProjectDesign + buildShipped
E-commerce storefront for a Kenyan eyewear retailer with three brands and a single checkout.
- TypeScript
- Next.js
- E-commerce
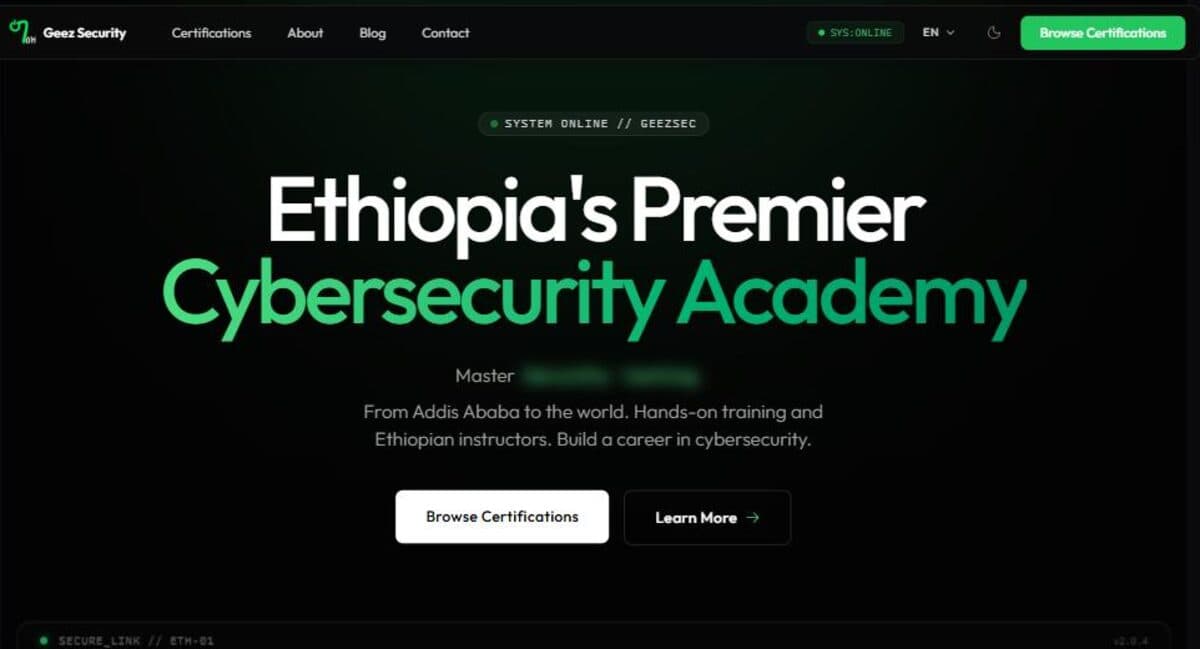
Geez Security
ProjectDesign + buildShipped
Bilingual cybersecurity academy for Ethiopia with certification tracks and course modules.
- TypeScript
- Next.js
- Security education
Open source and upstream06
better-middleware
PluginFramework-agnostic authentication middleware for Better Auth with session validation, caching, and typed errors.
AuthorOngoing
- TypeScript
- Better Auth
- Security
better-waitlist
PluginWaitlist plugin for Better Auth with email verification, queue management, and referrals.
Author · npmOngoing
- TypeScript
- Better Auth
- Plugin
haxurn-core
ProjectMonorepo foundation for a suite of cybersecurity tools and shared packages.
AuthorOngoing
- TypeScript
- Monorepo
- CTF
better-auth
Upstream contributionMerged upstream documentation for Better Auth's Fastify integration, plus the waitlist plugin proposal that became better-waitlist.
Contributor · fork → upstreamShipped
- TypeScript
- Open Source
- Authentication
better-hub
Upstream contributionTwo merged upstream pull requests on Better Auth's collaboration platform for humans and AI agents.
Contributor · fork → upstreamShipped
- TypeScript
- Open Source
- Browser extension
chapa-nodejs
Upstream contributionTwo merged upstream pull requests on the Node.js SDK for Chapa, Ethiopia's payment gateway.
Contributor · fork → upstreamShipped
- TypeScript
- Open Source
- Payments
03Craft
Two windows open at any given time.
My work happens in two places: a terminal, where I look for weaknesses, and an editor, where what I learn becomes typed, tested code.
01Find
I test my own routes the way an attacker would, before anyone else does.
02Fix
The fix goes where every request passes through, as typed, reusable code.
03Prove
Tests lock the fix in, and a second scan confirms the finding is gone.
pnpm scan:routes localhost:3000checking 14 routes for authGET /api/health publicGET /api/projects sessionPOST /api/admin/export no auth1 finding, 13 routes okpnpm test require-sessionrejects a missing sessionrejects an expired sessionlets a valid session through3 passedpnpm scan:routes localhost:30000 findings, 14 routes ok
// src/require-session.tsimport { APIError } from "./errors";import type { Auth } from "./types";export async function requireSession( auth: Auth, headers: Headers,) { const session = await auth.api .getSession({ headers }); if (!session) { throw new APIError("NO_SESSION"); } return session;}A condensed, illustrative session against my own local app. The code is a sketch of the kind of session check better-middleware provides, not an excerpt from it.
04Journey
A short timeline, with the milestones that matter.
01 / 06
First lines of code, self-taught
I wrote my first HTML and CSS with no course and no mentor, just documentation and a browser. I made small pages for friends and spent more time breaking them than styling them. Wanting to know what happens underneath a page set the direction for everything since.
02 / 06
First code: Python and CTF
I wrote my first real programs in Python and started competing in capture-the-flag events: reverse engineering, cryptography, binary exploitation. Once I could automate the work, I could do far more of it.
03 / 06
Red team at INSA
I joined the red team at INSA, Ethiopia's national security agency, and was trained by analysts with a decade of experience. The work: attack real systems with permission, test web applications, and write reports so the weaknesses get fixed. This is where security became my profession.
04 / 06
Left INSA for TypeScript development
In mid 2024 I left INSA and moved into software development full time: TypeScript everywhere, with React, Next.js, and Hono. Around the same time I started contributing to Better Auth and building plugins for it.
05 / 06
Co-founder and CTO, Solvix Labs PLC
In mid 2024 I co-founded Solvix Labs PLC and became its CTO. We build Axova, a commerce platform for Ethiopian merchants. The stack is TypeScript end to end, and security is built in from the start. I now ship the kind of systems I used to only test.
06 / 06
Started trading forex
I opened my first live account and began trading currency pairs and gold: swing and day trades, with the occasional scalp. Charts on TradingView, execution on MetaTrader 5. Before long I was writing code to test and automate the rules I trusted, which is where trading and engineering met.
·Credentials
On the record.
Where I work, what I contribute to, and where my capture the flag record lives.
INSA
Red team · offensive security
2024 → mid 2024
formerSolvix Labs PLC
Co-founder · CTO · Axova
mid 2024 → now
currentCapture the Flag
Web · crypto · pwn
80+ solves
ongoingOpen Source
Author · Better Auth plugins
waitlist · middleware · MIT
shipped
CTF standings03
Figures as listed on each platform when last checked.
Code, writing, and social profiles are listed in ContactOn file · haxurn
05Skills and stack
What I can do, and how well.
Building a company, trading the markets, writing software, and making music. Open any entry to read what it means in practice and where I have used it. Each one is rated on a four step scale, from learning it now to where I do my best work.
How to read the scale
- ExposureLearning it now.
- WorkingCan deliver with the documentation nearby.
- FluentCan deliver independently.
- DeepWhere I do my best work.
Building companies
Co-founder since 2024.
Company buildingFluent2024
Co-founded Solvix Labs PLC in mid 2024: setting direction with my co-founders, deciding what to build first, and turning a product idea into a registered company.
- solvix-labs
- strategy
- operations
Product strategyFluent2024
Choosing what Axova does and, harder, what it does not. Talking to merchants, scoping releases and cutting features so the core ships.
- axova
- roadmap
- scoping
Technical leadershipFluent2024
As CTO I own Axova's architecture, the engineering standards and the security posture, and I review the code that goes to production.
- cto
- architecture
- review
Go-to-marketWorking2025
Bringing a product to Ethiopian merchants: positioning, pricing conversations and onboarding. Still learning; selling is a different craft from building.
- sales
- onboarding
- positioning
Markets and trading
Trading forex since 2024.
Forex tradingFluent2024
Swing and day trades on the major pairs, with the occasional scalp when the session is moving. Charts on TradingView, execution on MetaTrader 5.
- majors
- swing
- intraday
Technical analysisFluent2024
Market structure, support and resistance, and session timing. I mark levels on the higher timeframes and only act on the lower ones.
- tradingview
- structure
- sessions
Risk managementFluent2024
Position size comes from the stop, never from the target. A fixed risk per trade and a journal of every entry keep the account alive through bad weeks.
- sizing
- journal
- drawdown
Algorithmic tradingWorking2024
Where the engineer and the trader meet: writing rules as code, back-testing them, and running the ones that hold up as bots on MetaTrader 5.
- mql5
- pine-script
- backtesting
Gold, indices and cryptoWorking2025
The same playbook applied beyond currencies: gold most of all, plus the major indices and crypto when they set up cleanly.
- xauusd
- indices
- crypto
What I build
Backed by shipped projects.
Full-stack web applicationsDeep2024
I design and build complete websites and web applications, from the database to the interface. Shipped examples: YES Multimedia, Mamy Opticians, Geez Security and the Axova web app.
- next.js
- postgres
- design
E-commerce and paymentsFluent2025
Storefronts, checkout flows, point-of-sale and payment integrations. Axova is a full commerce platform; Mamy Opticians is a live storefront; I contributed refunds to the Chapa payment SDK.
- axova
- checkout
- chapa
Authentication systemsDeep2024
Login, sessions, permissions and plugins on top of Better Auth. I publish two Better Auth packages on npm and have code merged into the framework itself.
- better-auth
- sessions
- npm
APIs and backend servicesDeep2024
Typed HTTP APIs and background services with Hono, tRPC, PostgreSQL and Redis queues. Most of Axova's services follow this pattern.
- hono
- trpc
- bullmq
Mobile appsFluent2025
Cross-platform iOS and Android apps with React Native and Expo. Nine apps so far, including Axova POS, Axova Go and Axova Marketplace.
- expo
- react-native
- eas
Cloud infrastructureFluent2025
Provisioning and running production systems on AWS with Terraform, Kubernetes and Helm: clusters, databases, caches, storage and CI/CD pipelines for Axova.
- aws
- terraform
- kubernetes
Cybersecurity
Practising since 2022.
Web penetration testingDeep2022
I test web applications for security weaknesses and write reports that developers can act on. It was my day-to-day work on INSA's red team, and I still apply it to everything I ship.
- burp
- recon
- authz
Red team operationsFluent2022
Authorised offensive engagements against real systems: planning, exploitation, documenting the path in, and briefing the people who need to close it.
- insa
- engagements
- reporting
Secure developmentDeep2022
Building software so it is hard to attack in the first place: threat modelling, secure code review and fixing whole classes of bugs rather than single instances.
- appsec
- threat-model
- code-review
Applied cryptographyFluent2022
Practical understanding of how encryption is used and misused: padding oracles, reused nonces, weak key handling. Mostly learned by breaking it in CTFs.
- ctf
- rsa
- aes
Reverse engineeringFluent2022
Taking compiled programs apart in Ghidra to find out what they really do, as opposed to what their documentation says.
- ghidra
- static-analysis
- x86
Binary exploitationWorking2022
Memory-corruption exploits and ROP chains in CTF settings. Comfortable with the fundamentals; modern mitigations still keep me humble.
- pwn
- rop
- gdb
Languages and frameworks
Writing code since 2022.
TypeScript / JavaScriptDeep2022
My primary language, used in strict mode across 43 repositories. I write the types first and treat them as the specification.
- strict-mode
- zod
- node
React / Next.jsDeep2022
Every shipped site runs on Next.js. Server components by default, client code only where the browser genuinely needs it.
- app-router
- rsc
- tailwind
PythonDeep2022
The first language I became fluent in. My choice for security tooling, automation and anything that has to exist by tonight.
- scripting
- automation
- ctf-tooling
HTML / CSSFluent2022
Where I started. Semantic markup, accessible focus states and a token-driven Tailwind setup like the one behind this site.
- tailwind-v4
- a11y
- layout
HonoFluent2022
Small, fully typed web services. Most of my backends now start as a Hono router.
- edge
- rpc
- middleware
BashFluent2022
The glue between everything else: scripts, CI steps and my dotfiles.
- pipes
- tooling
- ci
C / C++Working2022
I read far more of it than I write, usually to understand where a program fails. bhnet, my network utility, is written in C.
- memory
- source-dive
- pwn
Design and brand
Behind every interface I ship.
UI / UX designFluent2024
Designing the screens before building them: flows, hierarchy and states. Axova's merchant apps and this portfolio were designed by me.
- figma
- flows
- systems
Brand identityWorking2025
Names, marks, colour and voice for products and client sites, so a small company looks as considered as a large one.
- identity
- type
- voice
Music production
Learning, on weekends.
FL StudioExposure2025
Most Sundays. Still learning the fundamentals of arrangement and mixing.
- fl-studio
- arrangement
- mixing
Beat makingExposure2025
Loops that have not yet become finished songs. Finishing them is the current goal.
- drums
- sampling
- groove
Sound designExposure2026
Shaping sounds until they feel deliberate rather than accidental.
- synthesis
- fx
- texture
The tools behind the work.
Every tool here appears in my repositories. The note under each name says where I use it.
Languages
08 entries
- TypeScript43 repositories · primary language
- JavaScript42 repositories
- Python14 repositories · CTF tooling, automation
- Bash10 repositories · scripts, dotfiles
- Dart / FlutterAxova Rider mobile app
- Go2 repositories · services
- Cbhnet network utility · exploitation
- Solidityvoting-dapp
Frameworks & libraries
11 entries
- Next.js10 projects · every shipped site
- React12 projects
- Tailwind CSS12 projects · v4, token-driven
- Hono5 projects · typed API edges
- tRPC5 projects · end-to-end types
- TanStack Query8 projects · server state
- Zod16 projects · every system boundary
- Radix / shadcn7 projects · accessible primitives
- GSAPThis site · scroll choreography
- React Native9 apps · Axova POS, Go, Hub, Link, Marketplace
- Expo9 apps · EAS builds, Expo Router
Data & auth
07 entries
- PostgreSQLAxova, Geez Security, SchoolHub
- Prisma4 projects
- Drizzle ORM5 projects
- Neon4 projects · serverless Postgres
- SupabaseMamy Opticians
- Redis · BullMQAxova · queues and caching
- Better Auth7 projects · 2 published plugins · upstream contributor
Infrastructure
15 entries
 AWSAxova production + staging · SDK in 4 repos
 Amazon EKSAxova cluster · Karpenter autoscaling
 Amazon RDSPostgres + RDS Proxy · Axova
 S3 · CloudFrontMedia storage and CDN · Axova, Geez Security, Siranet
 ElastiCacheRedis for queues and sessions · Axova
 VPC · IAM · WAFNetwork, identity and edge security modules · Axova
 Secrets ManagerExternal Secrets into the cluster · Axova
- KubernetesHelm charts, HPA, network policies · Axova
- HelmPer-app charts, staging + production values · Axova
- Terraform15 modules · bootstrap, staging, production · Axova
- Docker7 Dockerfiles · Compose for local stacks
- Vercel5 live sites
- RailwayAxova services
- GitHub ActionsCI on Axova, Geez Security, this site
- Turborepo · NxMonorepos: Axova, Siranet, Karivo
Tooling & security
08 entries
- BunDefault runtime and package manager
- pnpmAxova monorepo, this site
- Vitest5 projects
- Oxlint · Oxfmt7 projects · lint and format
- Neovim · tmux · zshdotfiles · daily editor
- GitEvery project
- Burp SuiteWeb penetration testing
- LinuxPrimary OS · servers
Counts from a gh audit of my repositoriesrev · 2026.09
07GitHub
Every green cell is a small win.
A year of commits, pulled live from my public GitHub profile.
08Contact
Get in touch. I read every message.
Email is fastest. I usually reply within one or two days. GitHub and Instagram work too.
- Primary · emailhaxurn@gmail.comReply · 24–48h
- GitHub@haxurn (opens in a new tab)
- Instagram@haxurn (opens in a new tab)
- Discord@haxurn · Handle only, no public link
- Download résuméPDF
Based in · Addis Ababa, EthiopiaAfrica/Addis_Ababa
Elsewhere13
- npmcode~haxurn3 published packages · better-waitlist, better-middleware, conduithub (opens in a new tab)
- GitLabcode@haxurnMirror and private work (opens in a new tab)
- LeetCodecodehaxurnAlgorithm practice (opens in a new tab)
- CodeforcescodehaxurnCompetitive programming (opens in a new tab)
- TryHackMectfhaxurnLevel 65 · Guru · top 2% · 114 rooms · 15 badges (opens in a new tab)
- Hack The BoxctfhaxurnHacker rank · global rank 1049 (opens in a new tab)
- Buna Byte CTFctfhaxurnEthiopian CTF platform · 17 solves (opens in a new tab)
- Hugging FacecodehaxurnModels and experiments (opens in a new tab)
- DEV Communitywriting@haxurnTechnical writing (opens in a new tab)
- Mediumwriting@haxurnLonger-form essays (opens in a new tab)
- LinkedInsocialsamsontesfayeWork history and Solvix Labs (opens in a new tab)
- Xsocial@haxurnNotes in public (opens in a new tab)
- Telegramsocial@haxurnDirect messages (opens in a new tab)